Why are CISOs moving towards continuous identity assurance?
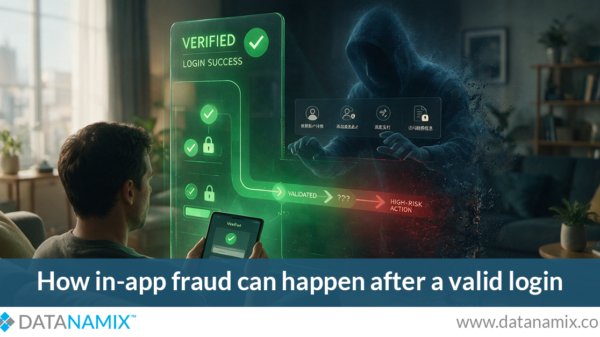
One reason is that a successful login only establishes identity at a particular moment, while important digital actions may take place throughout the rest of the session.
The answer to “Why are CISOs moving towards continuous identity assurance?” also reflects the wider pressure on security leaders to strengthen identity controls without discarding existing technology investments. Continuous identity assurance can add another identity signal to the authentication, device, transaction and fraud controls already in use.
Unauthorised access remains a significant concern
The preliminary 2026 ITWeb Brainstorm CISO Survey found that 51% of respondents identified unauthorised access or hacking as a leading cyber risk.
The survey also reported phishing as the most frequently experienced security incident and found that 28.3% of respondents had experienced identity theft during the preceding year.
For chief information security officers, these risks create a broader question: how long should the identity confidence established at login continue without additional context?
Login is one point in a longer journey
Authentication helps determine whether access should be granted. Once the user is inside the application, however, the consequences of their actions can change.
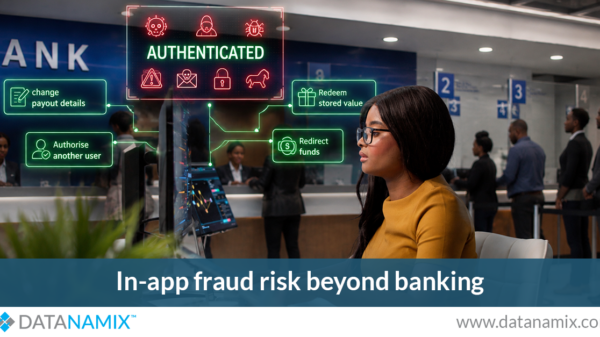
Viewing information is different from changing account details, adding a new payment destination, approving a transaction or granting another person access.
This is why identity assurance can be matched to the action. The organisation may rely on its existing controls for ordinary activity and require greater identity confidence when the potential consequence increases.
Existing security investments remain important
Continuous identity assurance is not a reason to abandon identity providers, multi-factor authentication, device controls, transaction monitoring or fraud-detection systems.
These technologies address different risks. Authentication protects access. Device controls provide information about the environment. Transaction monitoring identifies unusual activity. Continuous identity assurance adds context about who remains present during the session.
The value comes from combining these controls rather than treating one of them as a complete solution.
Continuous identity assurance supports risk-based decisions
Applying the same control to every user action can create unnecessary friction. Applying no additional assurance after login may leave important actions relying too heavily on the original check.
A risk-based approach allows security and product teams to identify the actions where more identity context could materially improve the decision.
The organisation also retains control over the response. Depending on the action and available evidence, it may continue the session, request another authentication factor, pause the action, generate an alert or refer it for review.
Identity assurance is not the same as fraud detection
Continuous identity assurance helps establish whether the authorised person remains present. It does not determine whether that person is being manipulated, whether the device contains malware or whether a transaction is commercially sensible.
CISOs therefore need to position it within a wider control environment that includes device security, behavioural analytics, transaction monitoring, customer education and incident response.
This distinction keeps the role of the technology clear and avoids relying on a biometric signal as the only basis for a sensitive decision.
The role of Continuous Facial Recognition with Liveness
Continuous Facial Recognition with Liveness is designed to extend identity assurance throughout a digital session while working alongside existing authentication and fraud controls.
Datanamix provides the technology to South African organisations. Powered by the YEO Continuous Facial Recognition SDK, it can support security strategies that require greater confidence in who is present during higher-risk digital actions.
Contact Datanamix to discuss where Continuous Facial Recognition with Liveness could fit into your existing identity and security environment.